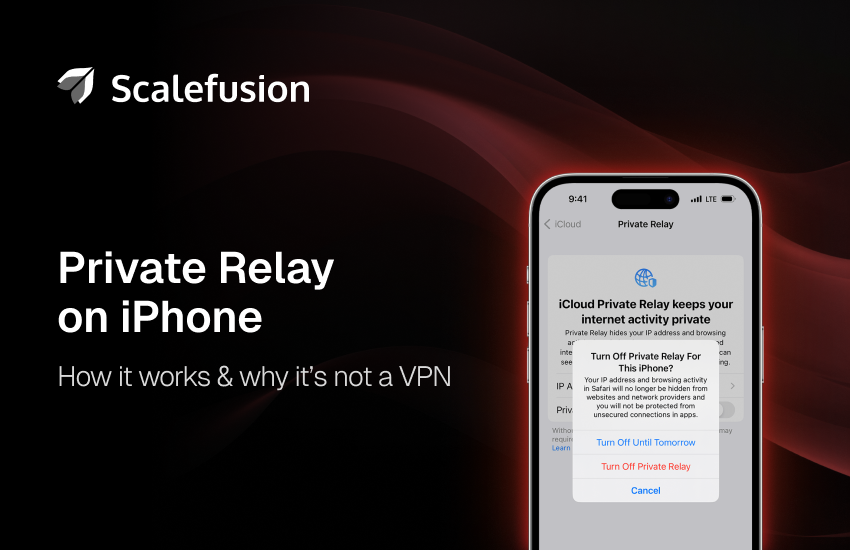
iCloud Private Relay is an internet privacy service included with iCloud+ that helps prevent websites and network providers from connecting your IP address with your Safari browsing activity. It routes supported traffic through two separate internet relays, so no single party, including Apple, can see both who you are and which websites you visit.
Private Relay is available on supported iPhone, iPad, Mac, and Apple Vision Pro devices. It improves browsing privacy, but it is not a full-device VPN and does not protect every type of internet traffic.nd stopping your network provider from seeing the sites you visit.
Key Takeaways
- Private Relay protects browsing privacy: It hides your original IP address from destination websites and encrypts DNS information associated with supported traffic.
- It uses two separate relays: Apple operates the first relay, while a different provider handles the second, separating your identity from your browsing destination.
- It is not a VPN: Private Relay does not provide the same device-wide traffic tunneling, server selection, or enterprise connectivity features as a VPN.
- Coverage has limits: Apple says it protects Safari browsing, DNS resolution queries, and insecure HTTP app traffic.
- Apple offers several related controls: Private Relay, Hide IP Address, Show IP Address, and Limit IP Address Tracking do different things.
- IT teams need to account for it: Private Relay can affect DNS filtering, traffic auditing, IP-based controls, and some enterprise network configurations.
What Is iCloud Private Relay and How Does It Work?
iCloud Private Relay works by separating two pieces of information that are normally available during web browsing: your IP address and the website you are visiting.
Normally, your network provider can see your IP address and potentially information such as DNS requests, while the destination website can see the public IP address used to connect to it.
Private Relay changes that path.
Step 1: Your Request Is Protected
When supported traffic leaves your device, DNS information is encrypted so your network provider cannot use those requests to determine which website you are trying to reach.
Step 2: Traffic Reaches Apple’s First Relay
The first relay is operated by Apple.
It can see your original IP address because it needs to know where the connection came from. However, your DNS records are encrypted, so the first relay cannot see the website you want to visit.
Step 3: A Second Relay Receives the Request
The request then goes to a second relay operated by another provider.
That relay can determine the requested destination, but it does not receive your original IP address. Instead, it assigns a temporary relay IP.
Step 4: The Website Receives the Relay IP
The destination website sees the temporary Private Relay IP rather than your original public IP address.
The result is the important part: one relay knows who you are but not where you’re going, while the other knows where you’re going but not your original IP address.
Apple describes this as a multi-hop architecture designed so that no single participant can associate a user’s identity with their browsing activity. Apple’s explanation of iCloud Private Relay
What Does iCloud Private Relay Actually Protect?
Private Relay primarily protects web browsing in Safari, but saying that it protects “Safari only” is slightly too simplistic.
According to Apple’s developer documentation, Private Relay protects:
- Safari web browsing
- DNS resolution queries
- Insecure HTTP traffic from apps
The important distinction is that Private Relay is not a universal encrypted tunnel for every application and connection on an Apple device. Apple Developer guidance on Private Relay traffic
That means you should not assume traffic from Chrome, Firefox, enterprise applications, VPN connections, or apps using their own networking mechanisms receives the same protection as Safari browsing.
Does iCloud Private Relay Hide Your IP Address?
Yes. Private Relay hides your original IP address from websites receiving supported traffic and replaces it with a relay IP address.
It does not, however, make your original IP address invisible everywhere.
Your internet provider still knows your IP address because it provides your network connection, and Apple’s first relay also receives it. What those parties cannot see through Private Relay is the destination associated with the encrypted request.
Apple also preserves approximate location information so websites can continue providing relevant regional content.
Users can choose between:
- Maintain General Location: Keeps enough regional information for locally relevant content.
- Use Country and Time Zone: Provides a broader location and makes your location less precise.
So Private Relay is designed to reduce IP-based tracking. It is not designed to make an iPhone in India appear to be browsing from the US, UK, or another manually selected country.
iCloud Private Relay vs. VPN: What’s the Difference?
iCloud Private Relay and VPNs can both prevent destination websites from seeing your original IP address, but they are built for different purposes.
| Feature | iCloud Private Relay | VPN |
|---|---|---|
| Main purpose | Safari and browsing privacy | Private or secure network connectivity |
| Original IP hidden | Yes, for supported traffic | Usually yes |
| Traffic coverage | Limited | Usually device-wide or configurable |
| Architecture | Two independent relays | Usually one VPN provider |
| Select another country | No | Usually |
| Protect third-party browsers | Not in the same way as Safari | Usually |
| Enterprise network access | No | Often |
| Included with | iCloud+ | Separate service in most cases |
The two-relay architecture is particularly important. With a conventional VPN, the VPN provider may technically be able to associate your connection with its destination. Private Relay deliberately divides that knowledge between separate entities.
So, iCloud Private Relay is not Apple’s version of a traditional VPN.
What Are the Benefits and Limitations of iCloud Private Relay?
Private Relay’s biggest advantage is simplicity. Once enabled, it adds IP and DNS privacy to supported browsing without requiring users to manually connect to a server whenever they open Safari.
It also makes cross-site profiling based on an IP address more difficult because websites receive a relay address instead of the user’s original address.
There are trade-offs, though.
Private Relay:
- Doesn’t provide full-device VPN protection
- Doesn’t let you choose a specific country or VPN server
- Isn’t available in every country or region
- Can cause additional verification on websites using IP-based fraud controls
- May conflict with certain VPN, filtering, parental-control, or enterprise networking configurations
- Can behave differently on networks that require traffic auditing or filtering
Some speed tests may also report different results while Private Relay is enabled. Apple explains that conventional speed tests often use multiple simultaneous connections, while Private Relay uses a secure connection architecture that can affect the reported throughput without producing an equivalent reduction in everyday browsing performance.
iCloud Private Relay vs. Hide IP Address vs. Limit IP Address Tracking
This is where Apple’s terminology gets confusing.
iCloud Private Relay is the iCloud+ privacy service that routes supported traffic through Apple’s dual-relay architecture.
Hide IP Address is a Safari privacy setting. Current Apple documentation says eligible iCloud+ subscribers can use it to hide their IP address from trackers and websites, while Safari can also protect against known trackers.
Limit IP Address Tracking controls whether Private Relay operates on a particular network. For example, you can disable it for one Wi-Fi network without completely turning off Private Relay on the device.
Show IP Address is different again. If one website isn’t working correctly because it relies on IP filtering, monitoring, or rate limiting, Safari can temporarily expose your IP address to that specific website while Private Relay remains active elsewhere.
In short:
Private Relay = service
Hide IP Address = Safari privacy control
Limit IP Address Tracking = network-specific control
Show IP Address = temporary website exception
That distinction makes troubleshooting Private Relay much easier.
How to Turn On iCloud Private Relay on iPhone or iPad
To enable Private Relay:
- Open Settings.
- Tap your name.
- Select iCloud.
- Tap Private Relay.
- Turn Private Relay on.
You can also open IP Address Location to decide whether websites receive your general location or only your country and time zone.
An active iCloud+ subscription is required.
How to Turn Off Private Relay for a Website or Network
You don’t always need to disable Private Relay completely when something stops working.
For a problematic website, Safari lets you use Show IP Address temporarily. Your IP remains visible to that website until you leave it or close its Safari tab, while Private Relay continues working for other sites.
For a Wi-Fi network, go to:
Settings > Wi-Fi > Network settings > Limit IP Address Tracking
For cellular connections, the setting is available under the relevant cellular data options.
This per-network approach is useful when a business, school, hotel, or filtered network isn’t compatible with Private Relay.
How Does iCloud Private Relay Affect IT Admins?
Private Relay becomes particularly relevant in organizations that rely on the network itself for security enforcement.
Because supported requests use encrypted DNS and relay IP addresses, Private Relay can affect:
- DNS-based web filtering
- Browsing visibility and network auditing
- IP-based access policies
- Fraud and rate-limiting systems
- Proxy-based controls
- Some compliance monitoring workflows
Apple specifically acknowledges that business and education networks may need to audit network traffic or perform network-based filtering. Network administrators can signal that Private Relay should not be used by returning the appropriate DNS response for Apple’s mask.icloud.com and mask-h2.icloud.com hostnames.
Web administrators should also avoid assuming that many connections from the same Private Relay IP represent one person. Apple notes that relay IP addresses may be shared among multiple users in the same area.
For managed Apple deployments, the practical question is therefore not simply “Should Private Relay be blocked?” It is whether your security controls depend on network-level visibility or whether comparable controls already operate on the endpoint.

FAQs
1. Is iCloud Private Relay the same as a VPN?
No. Private Relay protects specific browsing and network traffic using two separate relays, while a VPN typically routes much more of the device’s traffic through a VPN provider and may support server-location selection and corporate network access.
2. Does iCloud Private Relay work with Chrome?
Private Relay’s primary web-browsing protection is built around Safari. Third-party browsers such as Chrome and Firefox should not be assumed to receive the same Private Relay protection.
3. Does iCloud Private Relay slow down the internet?
Private Relay adds additional routing, and some speed tests may show lower throughput. Apple says these tests can behave differently because they commonly use multiple simultaneous connections, so the reported result may not directly reflect normal Safari browsing performance.
4. Can you use iCloud Private Relay with a VPN?
A VPN and Private Relay can both exist on an Apple device, but traffic routed through a VPN does not receive the same Private Relay path. VPN and network-extension configurations can also affect Private Relay behavior.
5. Should iCloud Private Relay be on or off?
For most personal Safari browsing, keeping Private Relay enabled provides additional IP and DNS privacy. An organization may need to restrict it on managed devices or specific networks when security, filtering, auditing, or access controls depend on network-level visibility.