

Ever seen a blue screen on starting a Windows device, in which the term ‘BitLocker’ appears in slick white fonts? For a personal desktop or laptop, you may find it a tad annoying, as you may already have a Windows Hello sign-in for secured access. Well, you’re free to disable the built-in version of BitLocker via ‘Manage BitLocker.’ But for organizations with a large fleet of company-owned Windows devices, this blue screen can make a lot of difference in terms of corporate data security. That’s the power of Windows BitLocker!

In this blog, we will shed some light on BitLocker and why it’s critical to manage this Windows feature on company-owned devices using a Unified Endpoint Management (UEM) solution to access your data securely.
What is BitLocker?
BitLocker is a full-disk encryption feature built into Microsoft Windows security that primarily focuses on safeguarding personal data on the device. This helps enhance security around the device by ensuring sensitive information is devoid of unauthorized access. It’s particularly helpful in case of lost or stolen devices.
BitLocker encryption achieves this by scrambling data on the drive, making it unreadable to anyone without the correct decryption key. This encryption and decryption process is seamless, ensuring that data is protected and the user experience remains unaffected.
Why is BitLocker important?
BitLocker is specifically designed to protect data at rest. This means it protects data when a device is powered off, lost, or stolen. It is an essential step in safeguarding sensitive data and plays a key role in maintaining security and compliance standards.
BitLocker helps organizations:
- Reduce the risk of data breaches from lost or stolen devices
- Meet compliance requirements such as GDPR, HIPAA, ISO 27001, and NIS2
- Protect sensitive customer and employee data
- Prevent unauthorized access to removed hard drives or SSDs
How does BitLocker disk encryption work?
BitLocker operates by encrypting your hard drive, converting data into a format that’s unreadable without the correct decryption key. This encryption is performed using industry-standard encryption algorithms, typically the Advanced Encryption Standard (AES) with 128-bit or 256-bit keys.
When you boot up your device, BitLocker requires authentication, which could be a password, a PIN, or even a USB key. Only after this verification will your drive be decrypted and accessible. Without the decryption key, the data on the drive appears as gibberish, making it unreadable and secure from unauthorized access.
The purpose of BitLocker is to safeguard both personal and business data. The powerful encryption algorithms it uses ensure sensitive files and data are shielded from unapproved access. Whether it’s financial documents, personal photos, or confidential business data, BitLocker is a robust line of defense for Windows Server.
Benefits of BitLocker encryption
The use of BitLocker encryption on your Windows devices is beneficial for two reasons:
1. Ensure data security
BitLocker is particularly valuable for businesses and individuals who handle sensitive data. Through drive encryption, you’re not just protecting your own information but also safeguarding client data, financial records, and confidential communications.
2. Adhere to compliance
For organizations, compliance with industry regulations is non-negotiable. BitLocker helps meet data protection standards like GDPR, HIPAA, and PCI-DSS by ensuring that sensitive data remains encrypted, even if devices are lost or stolen. This minimizes the risk of non-compliance penalties and ensures that your business maintains a strong reputation for data protection.
3. Prevent unauthorized access
BitLocker’s encryption ensures that only authorized users can access the data stored on a device. Even if a device falls into the wrong hands, encryption keys are required to decrypt the data, rendering it inaccessible to malicious actors.
4. Enhance device management
When combined with Windows’ native management tools or third-party MDM solutions, BitLocker encryption can be monitored and enforced across a device fleet. IT administrators can remotely manage encryption settings, track compliance status, and recover encrypted data if needed, streamlining security protocols.
What is a BitLocker recovery key?
A BitLocker recovery key is a 48-digit numerical backup passcode that allows you to unlock your BitLocker-encrypted drive if you can’t access it through a normal method (password, PIN, or TPM). If a device enters recovery mode, the recovery key is the only way to regain access to the data.
How to find a BitLocker recovery key?
There are several places where your recovery key might be, depending on the choice that was made when activating BitLocker.
- If the BitLocker recovery key is backed up to your Microsoft account, go to account.microsoft.com/devices/recoverykey (new window) and sign in using your Microsoft username and password.
- If your device was ever signed into an organization using a work or school account, the recovery key could be stored in that organization’s account to help protect your data. You might be able to access it directly, or you might need to contact the IT support for that organization to access your recovery key.
- If you use Windows Pro or Enterprise, you could have saved the key into either the Microsoft account (as above), a USB drive, a printed copy, or in the Active Directory of the organization for centralized management.
Read Full Article on : How to find a BitLocker recovery key?
Difference between BitLocker and Device Encryption
Device Encryption is a built-in Windows security feature. It is a simplified, user-friendly, and automated version of BitLocker, primarily aimed at consumer-grade protection. On the other hand, BitLocker is a more comprehensive solution offering advanced features and customization, typically used in enterprise environments.
Here’s a detailed comparison between the two:
| Aspect | BitLocker | Device Encryption |
|---|---|---|
| Availability | Windows Pro, Enterprise, and Education editions | Wider range of Windows editions, including Home |
| Target audience | Business professionals, advanced users, and IT admins | Windows Home users, non-enterprise users, and non-technical consumers |
| Encryption method | Offers AES encryption with 128-bit or 256-bit keys | AES encryption with 128-bit keys |
| User interaction | Requires manual enabling and configuration | Minimal; it is often enabled by default automatically on compatible hardware |
| Recovery key | Can be stored in a Microsoft account, Entra ID, USB flash drive, or as a text file/printout | Stored only in the user’s Microsoft account (cloud) |
| TPM requirement | Works with TPM 1.2 or higher; it can bypass TPM via Windows Group Policy, pre-boot password, or startup USB flash drive | Requires TPM 2.0 for automatic encryption; remains unavailable in the absence of TPM |
| Protection scope | Encrypts OS drives, fixed data drives, and removable data drives | Encrypts only the OS drive and fixed internal drives by default |
| Performance impact | Slight performance impact, customizable based on security requirements | Generally minimal, optimized for consumer devices |
| Management tools | Comprehensive, with Group Policy and PowerShell support | Basic, primarily through system settings |
| Customization | Advanced features like Network Unlock, multifactor authentication | Limited customization options |
How to turn on BitLocker on Windows devices
BitLocker is a robust encryption feature in Windows that secures data by encrypting drives and preventing unauthorized access. Enabling BitLocker can vary depending on your device and operating system. Here are the different methods to set up BitLocker on Windows:
Method 1: Enable BitLocker via Control Panel
Step 1: Open the Control Panel and navigate to “System and Security.”
Step 2: Click “BitLocker Drive Encryption.”
Step 3: Select the drive you wish to encrypt and click “Turn on BitLocker.”
Step 4: Follow the on-screen instructions to set a password or use a smart card to unlock the drive.
Step 5: Save the recovery key in a secure location and begin the encryption process.
Method 2: Enable BitLocker via Windows Settings
Step 1: Press the Windows Key + I to open your Settings app.
Step 2: In the search box at the top, type Manage BitLocker and press Enter to jump directly to the encryption settings.
Step 3: Locate your drive (usually labeled as your operating system drive or C:\).
Step 4: Click “Turn on BitLocker.”
Method 3. Enable BitLocker via Command Prompt
Step 1: Open the Command Prompt with administrative privileges.
Step 2: Use the following command to enable BitLocker on a specific drive: manage-bde -on <drive letter>:
Step 3: Follow the prompts to configure the encryption settings, such as choosing a key protector or recovery key setup method.
Method 4: Enable BitLocker via Group Policy
Step 1: Open the Group Policy Editor (gpedit.msc).
Step 2: Navigate to “Computer Configuration > Administrative Templates > Windows Components > BitLocker Drive Encryption.”
Step 3: Configure the relevant policies, such as enabling BitLocker for fixed data drives, operating system drives, or removable drives.
Step 4: Apply the changes and proceed to activate BitLocker via the Control Panel or Command Prompt.
Method 5. Enable BitLocker on the Windows Server
Step 1: Open the Server Manager dashboard.
Step 2: Use the “Add Roles and Features Wizard” to add the “BitLocker Drive Encryption” feature.
Step 3: Restart the server if prompted.
Step 4: After installation, use the Control Panel or Command Prompt to enable BitLocker on the desired drives.
Method 6. Enable BitLocker for Removable Drives
Step 1: Connect the removable drive to your system.
Step 2: Open “This PC,” right-click the removable drive, and select “Turn on BitLocker.”
Step 3: Choose an unlocking method (password or smart card) and follow the instructions to encrypt the drive.
How to enable BitLocker on Windows devices using Scalefusion MDM
Scalefusion MDM allows you to configure the different BitLocker Encryption settings from a single panel and enables you to push to multiple devices from one centralized dashboard. Here’s how it works:
Step 1: Sign in to the Scalefusion dashboard.
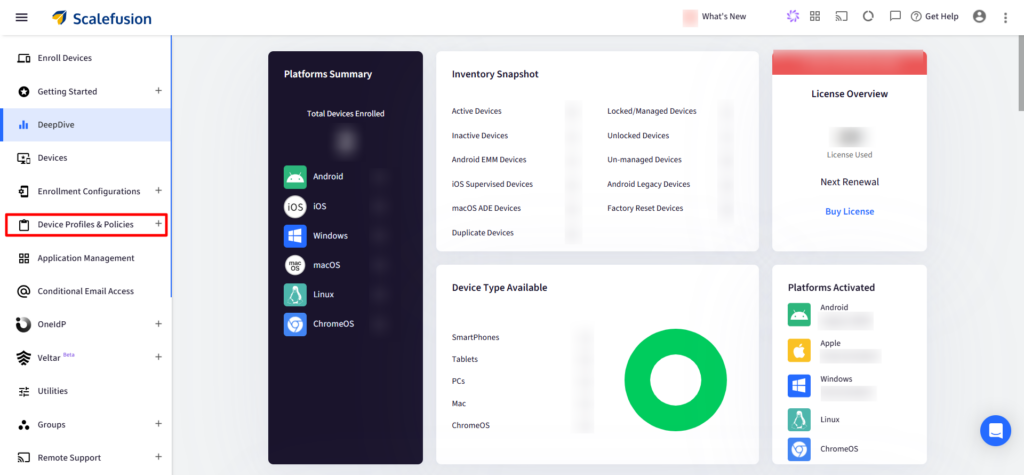
Step 2: Navigate to the ‘Device Profiles & Policies’ section on the dashboard.
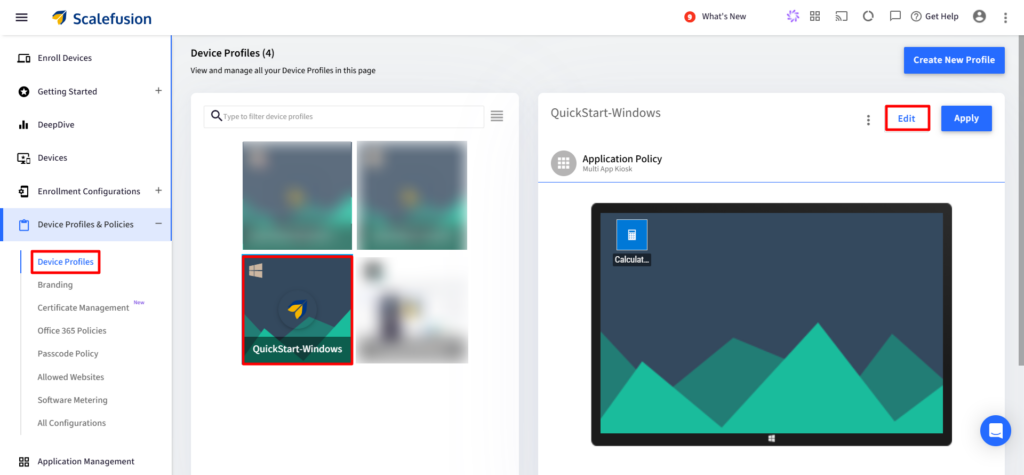
Step 3: Click the ‘Device Profiles’ tab. Now, create a new device profile for Windows. In case of an existing Windows profile, click the ‘Edit’ button.
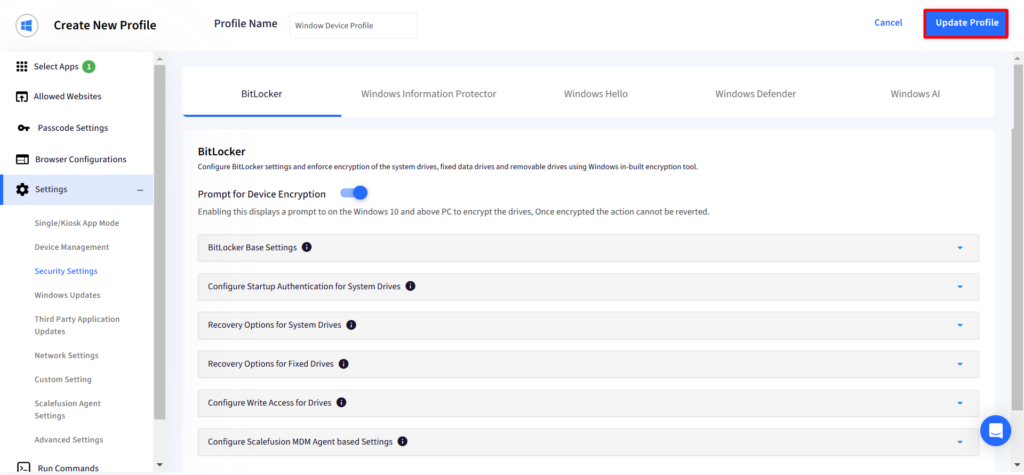
Step 4: Click the ‘Settings’ tab on the panel to your left. Go to ‘Security Settings’. Toggle on ‘Prompt for Device Encryption’ to turn on BitLocker.
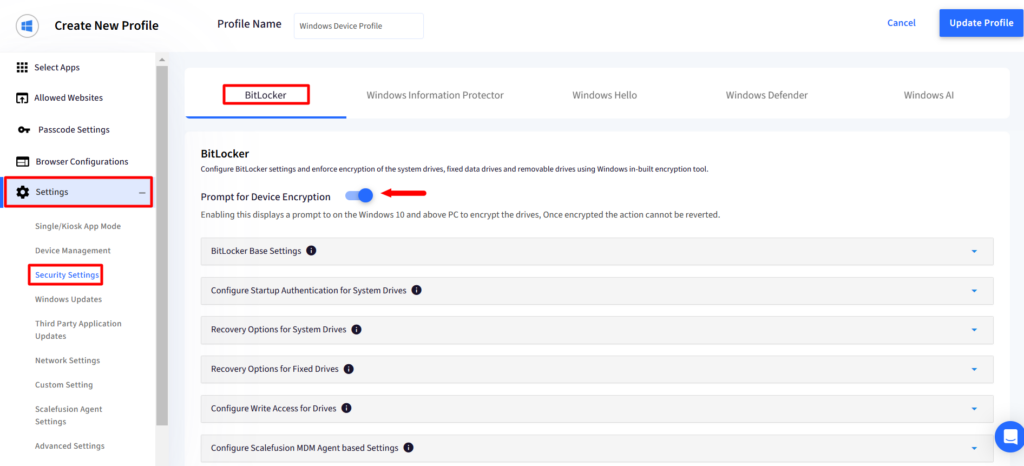
Step 5: Configure various BitLocker settings according to your requirements:
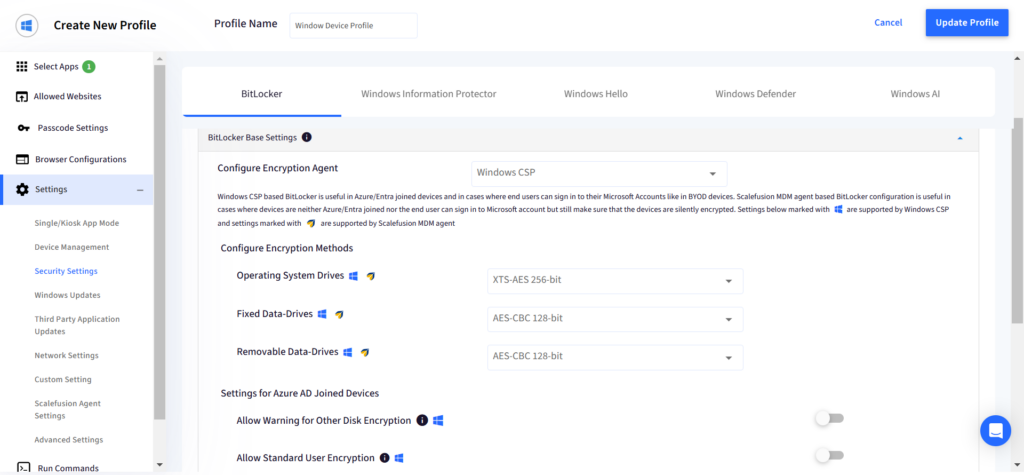
a. BitLocker Base Settings: Choose the encryption agent and method and the settings for Azure AD-joined devices.
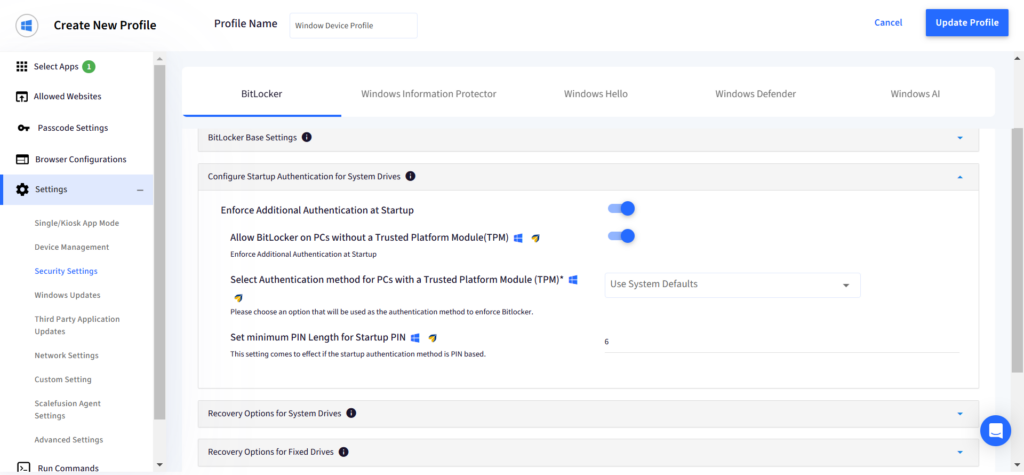
b. Configure Startup Authentication for System Drives: For computers without TPM, toggle on the ‘Allow BitLocker on PCs without a Trusted Platform Module (TPM)’ option. Set the authentication method and minimum length for the startup PIN.
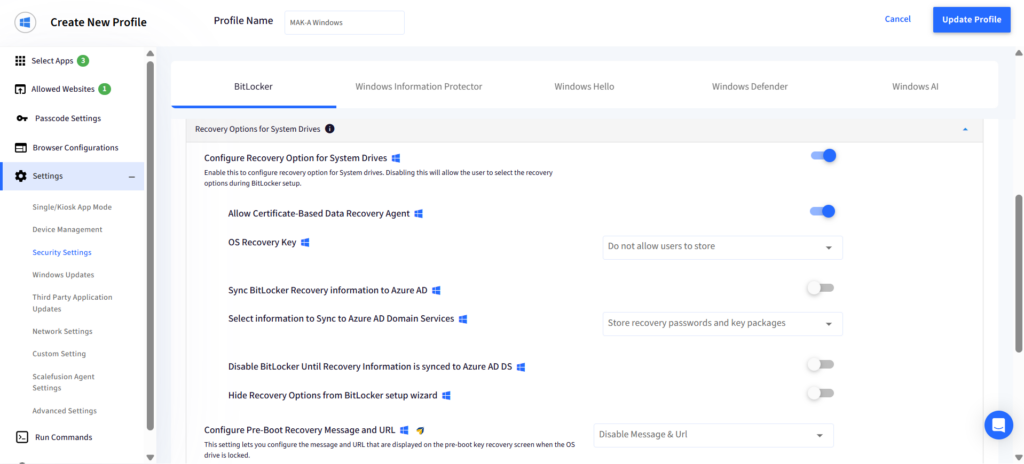
c. Recovery Options for System Drives: Set the policies for recovery and configure the preboot recovery message and URL. You can check the entire list of settings available here.
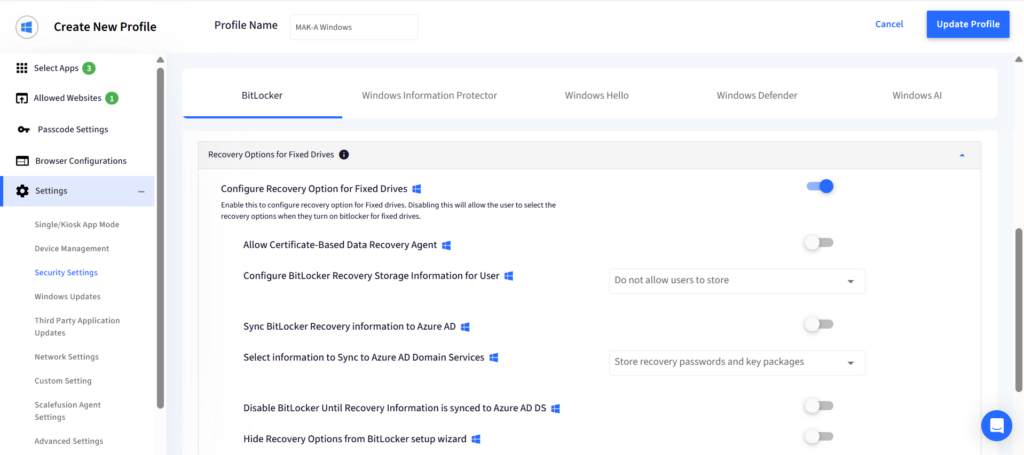
d. Recovery Options for Fixed Drives: These options are similar to those for system drives but are set for non-system drive partitions.
e. Configure Write Access for Drives: Disable the write access to the drives until they are encrypted, preventing any malware from reading/accessing the data on your drives.
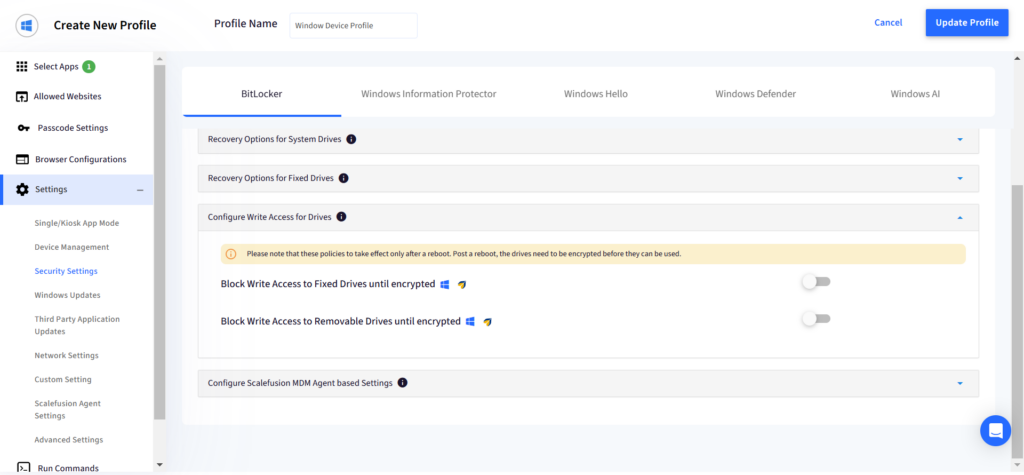
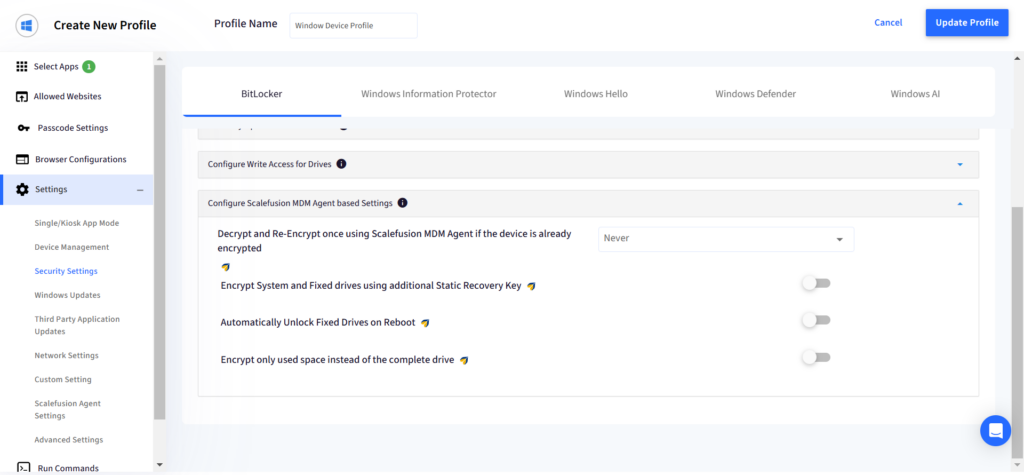
f. Configure Scalefusion MDM Agent-based Settings: Configure these settings if you have enabled BitLocker through the Scalefusion MDM Agent.
Step 6: Once you have completely configured BitLocker, click the ‘Update Profile’ button on the top-right corner of the screen.
Step 7: You will be redirected to the ‘Device Profiles’ page. Click ‘Apply’ to push the device profile to various device groups, user groups, or individual devices.
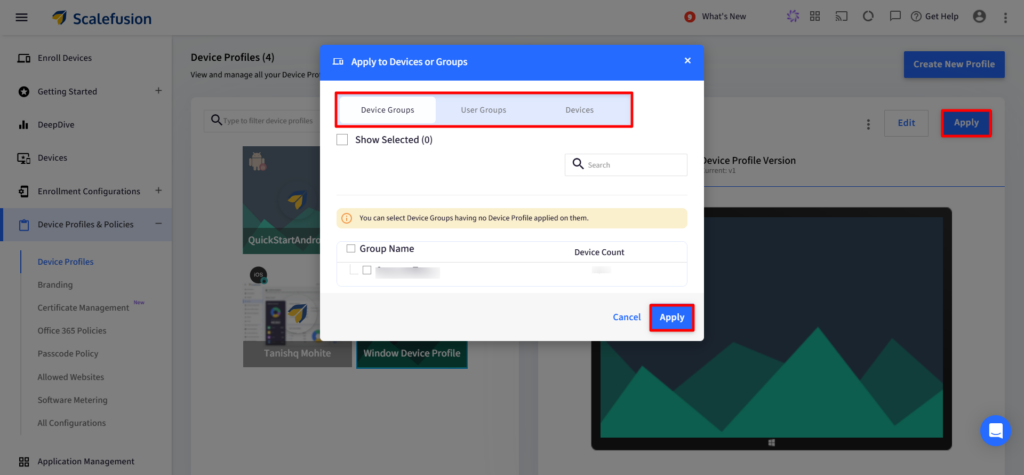
This enables BitLocker encryption on managed Windows devices and servers.
Best practices for using BitLocker
Deploying and managing BitLocker effectively requires a structured approach, particularly in larger or more complex environments comprising thousands of Windows devices. To ensure consistent security across the enterprise, here are a few best practices to keep in mind when implementing BitLocker:
1. Strategize deployment
It is necessary to develop a deployment plan to outline the steps needed to implement BitLocker on every Windows computer in your organization. This includes identifying which devices are to be encrypted, how the encryption keys will be managed, and how the deployment will be tested.
2. Assign group policies
By leveraging group policies, IT admins can set policies and preferences for multiple Windows devices from a centralized platform. This ensures that all devices are configured consistently and that the encryption keys are managed securely.
3. Enable UEFI Secure Boot and TPM
UEFI Secure Boot is a motherboard firmware standard that ensures a device boots using only trusted software signed by OEMs or OS vendors, protecting the boot chain from malware. TPM, available as a discrete chip or CPU firmware, acts as a hardware root of trust. It measures the integrity of the boot state and securely releases the BitLocker encryption keys only when the system is verified as safe and untampered.
By combining both, organizations ensure that data remains encrypted if the drive is moved to another machine or if the boot environment is modified.
4. Monitor and report encryption status
Create a comprehensive and consistent monitoring and reporting system for the encryption status of all Windows devices running BitLocker encryption. This makes it easy to identify when encryption faces any errors and provides reports on the overall encryption status of the organization.
5. Establish role-based training for users and admins
Security awareness training is critical to prevent data exposure and operational downtime. End-users should be trained on the importance of full-disk encryption, how to safely handle pre-boot PINs, and how to identify legitimate BitLocker recovery screens versus potential phishing or social engineering attempts.
IT admins must be trained on key escrow management, recovery procedures, and hardware lifecycle workflows. Specifically, admins must understand that completely disabling encryption unnecessarily exposes data and requires a lengthy re-encryption process.
Manage BitLocker on corporate devices with Scalefusion UEM
Deploying BitLocker within an organization necessitates a strategic approach to device management. From initial setup to ongoing maintenance, meticulous attention to detail is paramount. Using a UEM solution such as Scalefusion simplifies this process and provides a plethora of features, such as:
1. Centralized management
Adopting a centralized approach to BitLocker management streamlines operations, enhancing efficiency and accountability. Scalefusion enables IT admins to oversee BitLocker policies, monitor encryption status, and enforce device compliance across the organizational ecosystem.
2. Policy configuration
Crafting comprehensive BitLocker policies aligns encryption protocols with organizational security objectives. With Scalefusion, IT admins can tailor policies to enforce encryption standards, specify authentication mechanisms, and configure recovery options, thereby customizing BitLocker deployment according to unique organizational requirements.
3. Integration with existing systems
Scalefusion UEM seamlessly integrates BitLocker with existing device management to optimize workflow continuity and protect your data. IT admins can generate a BitLocker recovery key and enable the BitLocker function as the default for all managed Windows devices.
In addition, compatibility of a top-tier UEM software like Scalefusion with Active Directory facilitates user authentication, simplifying access management and enhancing user experience without compromising security standards.
To wrap it up
BitLocker is a smart and robust mechanism to protect corporate (and personal) data on Windows devices. Managing the deployment of BitLocker using a UEM solution like Scalefusion offers organizations plenty of flexibility to tighten their security posture. The icing on the cake is that Scalefusion holds a wide range of Windows device management capabilities that extend well beyond BitLocker.


FAQs
1. What is BitLocker drive encryption?
BitLocker drive encryption is a full-disk encryption capability built into Windows. It encrypts the entire file system, converting the storage volume into a secure, encrypted drive. When paired with MDM, it adds a crucial defense for remote and mobile devices. If an unauthorized party tries to access the device, recovery attempts will be required using a recovery password or key. This is vital for organizations looking to enforce consistent encryption in Windows across their fleet.
2. What is BitLocker used for?
BitLocker is primarily used to prevent unauthorized access to sensitive data by encrypting the entire file system on a drive. It’s especially important in MDM scenarios where devices may frequently connect to untrusted networks or travel between locations. With an encrypted drive, even if the device is compromised, data remains unreadable. Additionally, since the key is stored securely, often in the TPM or with Active Directory integration, data access remains protected even during recovery attempts.
3. What type of encryption does BitLocker use?
BitLocker uses Advanced Encryption Standard (AES) with 128-bit or 256-bit keys to secure data on the file system. This robust encryption is the cornerstone of modern encryption in Windows, providing reliable protection for organizational data. When a device is encrypted, the key is stored securely, and access to the encrypted drive requires authentication or a recovery password. This method ensures strong compliance with data protection policies while offering a user-friendly experience.
4. Should I turn on Windows BitLocker?
Yes, enabling BitLocker is highly recommended for both individuals and organizations. It transforms your device’s storage into an encrypted drive, securing the file system and preventing unauthorized access. Especially when managed through MDM, BitLocker enhances your security framework by adding another layer of encryption in Windows. If needed, you can always turn off BitLocker, but it’s advised to keep it on for ongoing protection of your sensitive data with BitLocker encryption. In case of access issues, a recovery password can be used or recovery attempts can be initiated to regain access without compromising data integrity.

