Automated patch management is the process of using software to identify missing patches, prioritize and test updates, deploy them according to predefined policies, and verify installation with minimal manual effort. It helps IT teams patch operating systems and applications consistently across large or distributed endpoint environments.
Instead of an administrator checking hundreds of devices individually, automated patch management turns patching into a policy-driven workflow: find the gap, decide how urgently it needs fixing, deploy the update, and confirm that it actually worked.
Key Takeaways
- Automates repetitive patching tasks: Automated patch management can handle discovery, patch acquisition, scheduling, deployment, retries, verification, and reporting.
- Reduces exposure time: Faster patch deployment reduces the window during which known vulnerabilities remain exploitable.
- Improves consistency: Policies apply the same patching rules across remote, on-premises, and distributed endpoints.
- Supports risk-based patching: Critical and actively exploited vulnerabilities can receive faster remediation than routine updates.
- Still requires human oversight: Sensitive systems, exceptions, failed patches, emergency changes, and rollback decisions may require administrator approval.

How Does Automated Patch Management Work?
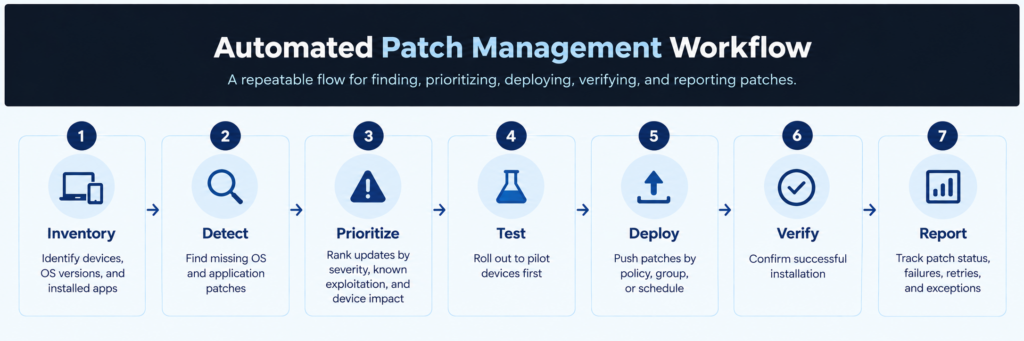
Automated patch management works by continuously discovering missing updates and moving approved patches through prioritization, testing, deployment, and verification according to rules set by IT administrators. covering both OS patch management and third-party application patching, through prioritization, testing, deployment, and verification according to rules set by IT administrators.
A typical workflow has five stages.
1. Discover Devices and Missing Patches
The system first maintains an inventory of endpoints, operating systems, installed applications, and software versions.
It then compares those versions against available vendor updates to determine which devices are missing patches.
Good inventory matters. You can’t patch a vulnerable application if you don’t know it’s installed.
2. Prioritize Patches Based on Risk
Not every missing patch deserves the same deadline.
A mature automated patch management process can consider factors such as:
- vulnerability severity
- known exploitation
- affected asset importance
- internet exposure
- application criticality
- available remediation deadlines
CISA specifically recommends using its Known Exploited Vulnerabilities Catalog as an input when prioritizing vulnerability remediation.
That distinction matters. A vulnerability already being exploited in the wild usually deserves a different response from a low-severity bug affecting an internal utility.
3. Test Patches
Automation should not mean deploying every update immediately to every endpoint.
Patches can first be released to a small test group or deployment ring. IT teams can check for application compatibility problems, installation failures, performance issues, or unexpected reboots before expanding deployment.
4. Schedule and Deploy Updates
Approved patches are then pushed according to defined policies.
Administrators might configure:
- IT test devices first
- a limited pilot group next
- general employee devices afterward
- business-critical systems during a separate maintenance window
Remote devices that are offline during deployment can be retried when they reconnect.
5. Verify Installation and Handle Failures
Successful deployment is not the same as successful remediation.
The platform should verify that the patch installed correctly and report devices that failed, remained offline, require rebooting, or still show the vulnerable software version.
NIST includes verification as a core part of enterprise patch management rather than treating installation as the final step.
Manual vs. Automated Patch Management
Both approaches ultimately aim to keep systems updated. The difference is how much repetitive work administrators must perform themselves.
| Area | Manual Patch Management | Automated Patch Management |
|---|---|---|
| Patch discovery | Admin checks vendors and systems | Software scans continuously or on schedule |
| Prioritization | Manual review | Policy/risk-based prioritization |
| Testing | Individually coordinated | Automated pilot groups or deployment rings |
| Deployment | Admin pushes patches manually | Scheduled policy-based deployment |
| Offline devices | Requires follow-up | Automatic retry when devices reconnect |
| Verification | Manual checks | Automated status validation |
| Reporting | Spreadsheets or separate reports | Centralized dashboards and audit reports |
| Scalability | Becomes harder as endpoints grow | Designed for large endpoint fleets |
Automation therefore doesn’t replace patch management. It automates repeatable parts of the patch-management process.
Why Is Automated Patch Management Important?
The biggest reason is simple: the number of vulnerabilities and endpoints IT teams must manage has grown faster than manual patching processes can comfortably handle.
The 2026 Verizon Data Breach Investigations Report found vulnerability exploitation represented 31% of known initial-access vectors in its breach dataset. It also reported that only 26% of critical vulnerabilities identified through CISA’s KEV catalog were fully remediated by organizations during 2025.
Automated patching can help organizations:
- shorten vulnerability remediation times
- reduce repetitive administrative work
- apply updates more consistently
- support remote and distributed endpoints
- maintain patch-compliance records
- reduce mistakes caused by manual processes
- schedule updates around business operations
- identify failed or missed deployments faster
NIST describes enterprise patch management as a form of preventive maintenance that organizations should operationalize and track as part of normal technology management.
What Should and Shouldn’t Be Automated?
The safest automated patch management strategy does not remove humans from every decision.
Automate tasks that are predictable, repetitive, and governed by clear policies:
- endpoint and software discovery
- missing-patch detection
- patch downloads
- routine prioritization
- deployment scheduling
- pilot-group rollouts
- retrying missed endpoints
- reboot notifications
- installation verification
- compliance reporting
Keep human approval available where business impact could be substantial.
For example, an IT team may require additional review before patching domain controllers, production servers, healthcare workstations, point-of-sale systems, or devices running business-critical legacy applications.
The goal is not maximum automation. It’s controlled automation.
Automated Patch Management Best Practices
A good automated patching program needs guardrails around the automation itself.
Prioritize actual exploitation risk. Don’t rely exclusively on severity scores. Combine vulnerability severity with information such as CISA’s KEV catalog, asset exposure, and business importance.
Deploy patches in rings. Start with IT or test devices before expanding to wider production groups. A bad patch affecting 10 pilot systems is easier to manage than one affecting 10,000 endpoints.
Define maintenance and reboot policies. Updates that require restarts should respect working hours, maintenance windows, and business-critical workloads.
Include third-party applications. Browsers, PDF readers, communication tools, runtimes, and other business applications need patching alongside the operating system.
Track exceptions. Every deferred update should have an owner, reason, and review date rather than remaining indefinitely excluded.
Measure outcomes rather than activity. Useful metrics include patch compliance, remediation time, deployment success rate, failed installations, overdue critical patches, and the percentage of endpoints still exposed to actively exploited vulnerabilities.
When Should you use UEM for Automated Patch Management?
Automated patch management can live in a standalone patching tool, a vulnerability management platform, an RMM tool, or a unified endpoint management platform.
A UEM-based approach makes sense when patching needs to connect with broader endpoint management. That usually includes device inventory, operating system visibility, policy enforcement, remote troubleshooting, compliance status, and device grouping.
Standalone patch tools can work well when the need is narrow: deploy patches and report status. But many IT teams need patching to sit alongside the rest of endpoint operations.
That is where UEM can help. Instead of treating patching as a separate workflow, IT teams can manage patch deployment alongside the controls they already use to manage devices.
With Scalefusion, IT teams can connect patch management with broader endpoint-management workflows. Scalefusion supports OS update and patch management across Windows, macOS, and Linux endpoints. For supported Windows and Linux devices, IT teams can also manage third-party application updates and patches.
Admins can configure update policies and schedules, monitor patch status, and use reporting to identify pending, installed, or failed updates. This keeps patching connected with the device visibility and management workflows IT teams already use across their endpoint environment.
Explore Scalefusion automated patch management solution to manage OS updates across Windows, macOS, and Linux and third-party application patches across supported Windows and Linux endpoints.
Final Thoughts
Automated patch management software turns patching from a series of repetitive administrative tasks into a repeatable, policy-driven process. It can continuously identify missing updates, prioritize remediation, stage deployments, patch endpoints, retry failures, and verify results without an administrator manually managing every step.
The most effective approach is not “patch everything automatically.” It is to automate predictable work while keeping human judgment around exceptions, critical systems, deployment risk, and business impact. That balance gives IT teams both speed and control.
FAQs
1. What is an automated patch management system?
An automated patch management system is software that identifies missing updates and automates tasks such as patch acquisition, testing, scheduling, deployment, verification, retries, and reporting. Administrators define policies that determine which devices receive particular patches and when deployments occur.
2. How does automated patch management improve security?
Automated patch management improves security by reducing the time known vulnerabilities remain unpatched. It continuously identifies missing updates and can accelerate deployment of high-risk or actively exploited vulnerabilities instead of waiting for administrators to manually identify and patch every affected endpoint.
3. Is automated patch management the same as vulnerability management?
No. Vulnerability management is the broader process of discovering, assessing, prioritizing, remediating, and monitoring security weaknesses. Patch management is one remediation method within that process. Some vulnerabilities may instead require configuration changes, compensating controls, software removal, or replacement.
4. Can automated patch management handle third-party applications?
Yes. Automated patch management platforms can support third-party applications in addition to operating-system updates. Coverage varies by solution, so IT teams should verify support for the browsers, productivity applications, communication tools, runtimes, and other software used in their environment.
5. Does automated patching eliminate the need for IT administrators?
No. Automated patching reduces repetitive administration but does not eliminate human oversight. IT teams still define policies, evaluate exceptions, manage sensitive systems, investigate failed deployments, approve high-impact changes, and decide when patches should be delayed or rolled back.